[Quick Bites] Load Balancers
In every tutorial the app runs on one server with one public IP, and that is fine until the server dies at 2am or a sale sends everyone to it at once. Real companies don't run on one.
This is part of my enterprise cloud architecture series. If you missed the intro, start here.

What is a load balancer?
Its a single entrypoint for traffic to be distributed to. Essentially a conveyor that sends packets wherever it needs to go based on rules or decisions. Human or Bot made.
Companies put one in front of their apps for three reasons:
- High Availability. One server dies, the others keep serving, and users don't notice.
- No cascading failure. Traffic is spread out instead of piling onto one machine.
- Additional Features. It can handle TLS termination (decrypt the traffic once at the front, so every server doesn't deal with certificates), and some can route by URL path, like
/apito one group of servers and/imagesto another.
L4 vs L7
The OSI model has seven layers, load balancers come only on 2
- Layer 4 (transport) knows IP addresses and ports, TCP and UDP. It doesn't care what is inside.
- Layer 7 (application) understands HTTP, so it can see the URL, the headers, the hostname.
Think of a courier who only reads the address on the parcel (L4) versus a receptionist who opens the parcel and decides which department it goes to (L7).
ALB vs NLB
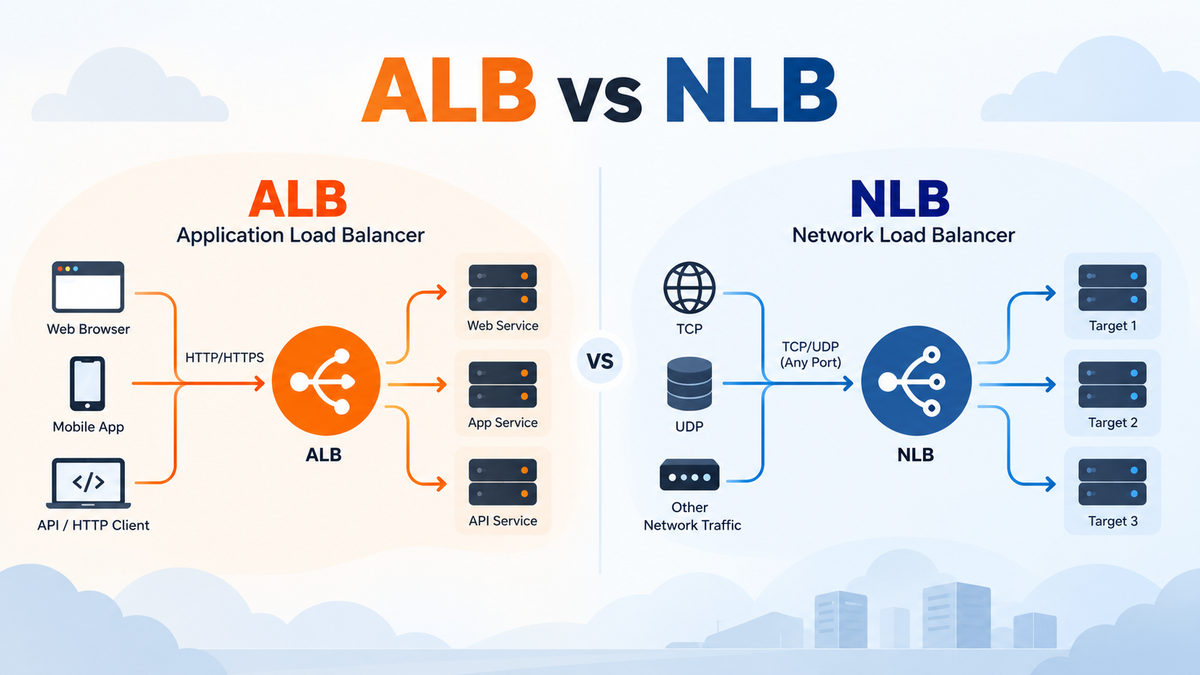
- ALB (Application Load Balancer) works at L7 for HTTP and HTTPS. It routes by path or hostname, so it is the default for web apps and APIs. The catch is that you get a DNS name, not a fixed IP, because the IPs behind it can change as it scales.
- NLB (Network Load Balancer) works at L4 for TCP, UDP and TLS. It is built for raw speed and can give you a fixed IP per availability zone, which matters when a partner needs to allowlist your address.
I'd start with an ALB and only reach for an NLB when one of those reasons shows up. If you need a fixed IP or private links, you can put an NLB in front of an ALB.
In an enterprise it is never one load balancer
We draw it as a single box, but behind it there are many. Usually one set per environment, per team or service, some facing the internet and some internal, only talking to other services. Each one is spread across at least two availability zones.
A common path looks like:
flowchart LR
  U([User]) --> CDN[CDN]
  CDN --> PALB[Public ALB]
  PALB --> APP[App servers]
  APP --> IALB[Internal ALB]
  IALB --> BE[Backend service]

  P([Partner needing a fixed IP]) -.-> NLB[NLB]
  NLB -.-> PALB
It also connects back to the CDN post. The load balancer is usually what the CDN treats as its origin.
The four pillars
| Pillar | The question | For load balancers |
|---|---|---|
| Security | Who can reach this? | Only the load balancer faces the internet, servers only accept traffic from it, TLS ends here |
| Reliability | What happens when it breaks? | Health checks pull a bad server out of rotation, and targets sit in more than one zone |
| Performance Efficiency | Is it fast enough, and is it the right tool? | ALB for web traffic, NLB for raw speed or non-HTTP |
| Cost Optimization | Where is the money going? | Every load balancer costs money, so don't spin up one per tiny service, share an ALB with routing rules. Traffic crossing zones can add data transfer charges too |
Next up: Firewall